FastAPI Todo Application — Live Production Deployment
A full-stack, multi-user task management application and REST API deployed publicly on Oracle Cloud Infrastructure (OCI). Engineered with asynchronous FastAPI, PostgreSQL via SQLAlchemy 2.0, Alembic migrations, dual-channel JWT authentication, HMAC-signed CSRF protection, and Caddy automated TLSv1.3.
Live Production Application Interface
Click any screenshot below to inspect the verified live production application interface running on Oracle Cloud Infrastructure:
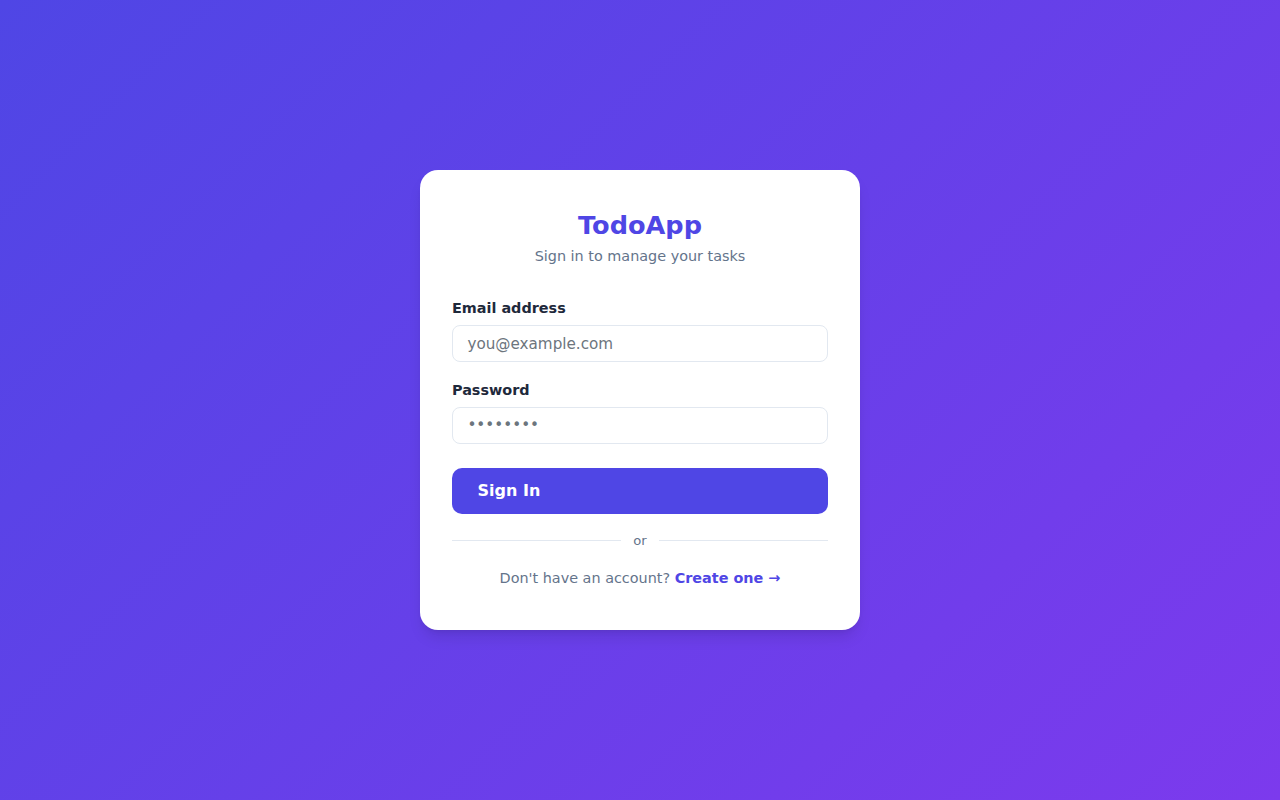
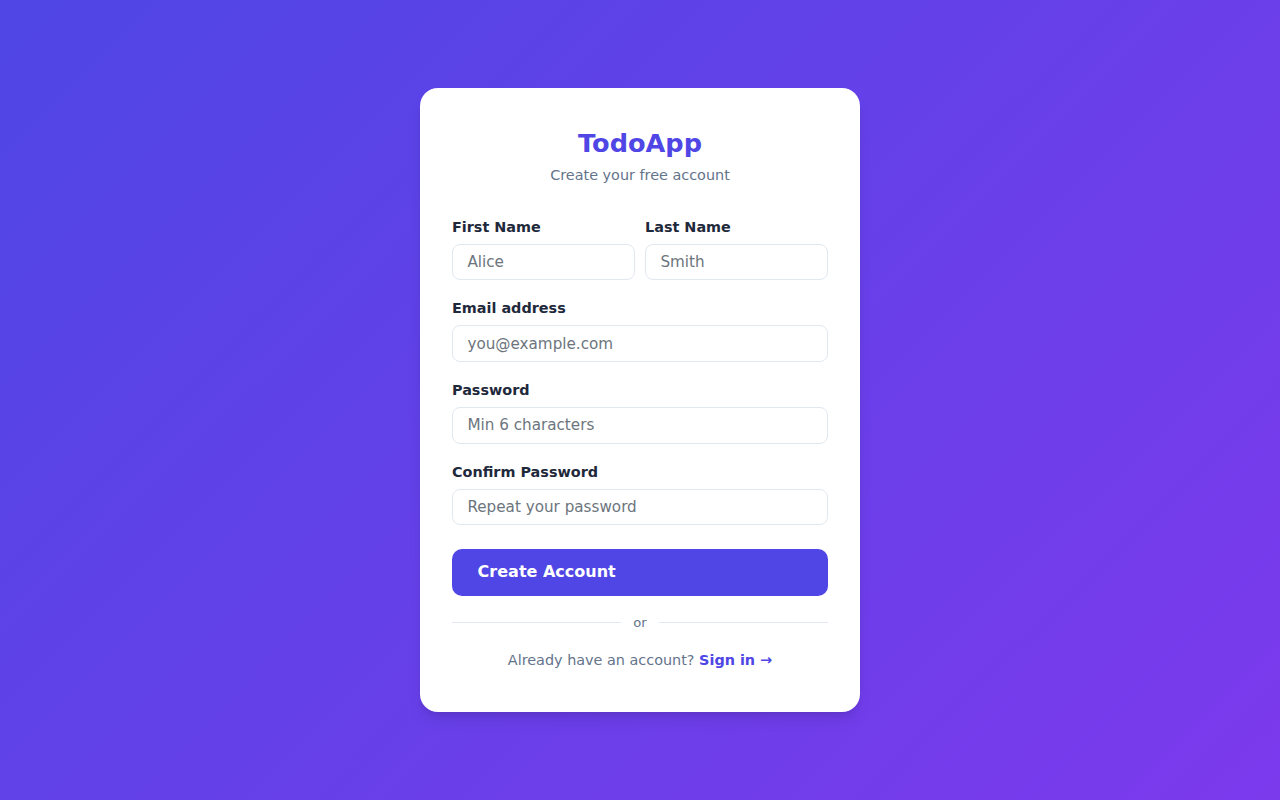
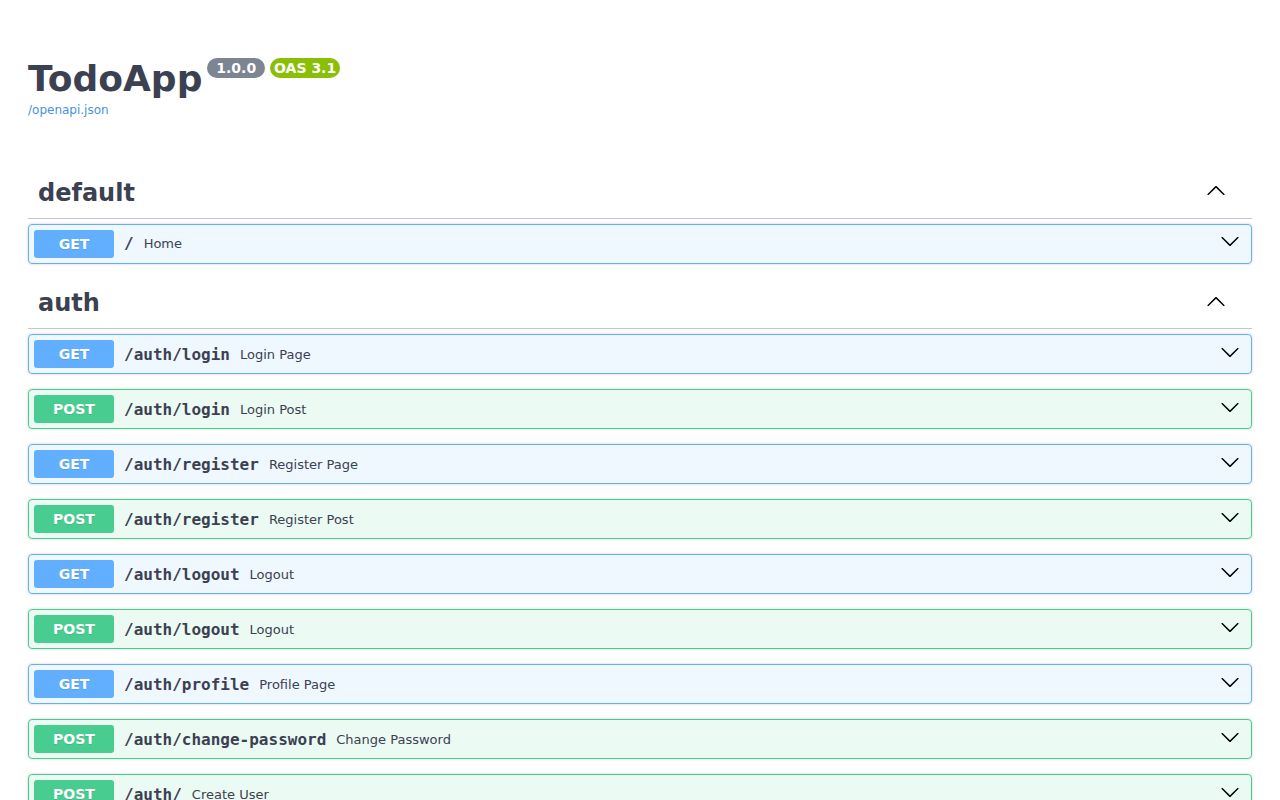
Framework & Application Architecture
The system is engineered as a clean, modular Python application with strict separation of concerns across data persistence, business logic, templates, and security middleware:
- Version Boundaries: The application itself is versioned as TodoApp v1.0.0, powered by the FastAPI framework (v0.139.2 / v0.141.x) running on Uvicorn v0.52.1.
- Relational Data Layer: Backed by SQLAlchemy 2.0 with fully typed declarative models (
UsersandTodos). Foreign key constraints enforce strict referential integrity withON DELETE CASCADEso deleting a user cleanly purges their associated todos. - Database Migrations: Managed via Alembic. The current head migration is
0002_reconcile_schema, which tightensNOT NULLconstraints, establishes server defaults (is_active=true,role='user',complete=false), and creates a performance index onowner_id. - Multi-Tenant Data Isolation: Every Todo query and mutation is strictly scoped at the database layer with
Todos.owner_id == current_user.id, guaranteeing that no user can access or tamper with another tenant's tasks.
Authentication & Security Engineering
Security was engineered from first principles rather than relying on default framework assumptions:
- Dual-Channel Authentication: Serves browser users via HTTP-only,
SameSite="lax",SecureJWT session cookies, while simultaneously exposing a JSON REST API authenticated via standardAuthorization: Bearer <token>headers viaPOST /auth/token/login. - HMAC-SHA256 CSRF Middleware: Custom HTTP middleware ensures every browser session holds a cryptographically signed CSRF cookie. State-changing POST requests require a matching hidden form input token, preventing cross-site request forgery.
- Password Security: User passwords are encrypted using
bcryptviapasslibwith individual salts; zero plaintext passwords are ever persisted or logged. - Role-Based Access Control (RBAC): Public user registration strictly assigns
role="user". Administrative endpoints (system statistics, user activation/deactivation) requirerole="admin". Deactivated users (is_active=False) are immediately blocked from logging in.
Production OCI Deployment & Systemd
Deployed on an Oracle Cloud Infrastructure (OCI) Compute Instance (VM.Standard.E2.1.Micro, 1GB RAM) in the ap-mumbai-1 region. Because micro-instances have strict memory limits, running heavy container orchestration engines risks Out-Of-Memory (OOM) failures. The application was engineered to run directly as a native Linux service:
[Unit]
Description=FastAPI Todo Application
After=network.target
[Service]
User=opc
WorkingDirectory=/home/opc/apps/todoapp/FASTAPI_PRAC
EnvironmentFile=/home/opc/apps/todoapp/FASTAPI_PRAC/.env
ExecStart=/home/opc/apps/todoapp/FASTAPI_PRAC/.venv/bin/uvicorn TodoApp.main:app --host 127.0.0.1 --port 8000 --workers 1
Restart=always
RestartSec=5s
[Install]
WantedBy=multi-user.target
Fronted by a Caddy v2 reverse proxy that automatically obtains and renews Let's Encrypt TLSv1.3 certificates via elliptic curve cryptography (prime256v1). Caddy handles HTTP/2 and HTTP/3 QUIC negotiation, gzip/zstd compression, and enforces security headers (HSTS, X-Content-Type-Options: nosniff, X-Frame-Options: DENY).
Automated Verification & Test Suite
The application codebase includes an automated test suite executed via pytest verifying functional correctness, tenant isolation, and security boundaries:
tests/test_admin.py::test_registration_cannot_create_admin_account PASSED
tests/test_admin.py::test_normal_user_cannot_access_admin_routes PASSED
tests/test_admin.py::test_admin_dashboard_stats_and_user_activation PASSED
tests/test_auth.py::test_successful_registration_api_and_login PASSED
tests/test_auth.py::test_successful_registration_html_flow PASSED
tests/test_auth.py::test_duplicate_registration_prevented PASSED
tests/test_auth.py::test_registration_password_validation PASSED
tests/test_auth.py::test_login_success_incorrect_password_and_logout PASSED
tests/test_auth.py::test_expired_and_invalid_jwt_rejected PASSED
tests/test_auth.py::test_inactive_user_cannot_login_or_access_routes PASSED
tests/test_auth.py::test_unauthorized_access_blocked PASSED
tests/test_auth.py::test_profile_and_password_change_with_csrf PASSED
tests/test_frontend.py::test_public_auth_pages_and_static_assets PASSED
tests/test_frontend.py::test_authenticated_dashboard_navigation_and_templates PASSED
tests/test_frontend.py::test_admin_navbar_link_visible_for_admin_only PASSED
tests/test_isolation.py::test_user_a_cannot_access_modify_or_delete_user_b_todos PASSED
tests/test_todos.py::test_todo_json_api_crud_and_validation PASSED
tests/test_todos.py::test_todo_html_crud_toggle_and_csrf PASSED
======================== 18 passed, 1 skipped in 9.63s =========================